
Charles Edwards, founder and CEO of Capriole Investments, has issued its most stardy warning to date on quantum computer science, arguing that bitcoin must migrate to post-sur-quantum signatures on an accelerated calendar or cope with the existential risk later this decade. “We have to upgrade Bitcoin to be quantum proof next year. 2026. Otherwise, we are fucked,” Edwards wrote early on Monday, degenerating a series of messages in which he supports “Q-Day is this decade.”
Could Bitcoin crash at $ 0?
Edwards’ thesis depends on the rapid compression of the resources necessary to execute the Shor algorithm against digital signatures of the Bitcoin Elliptical Courbe (ECDSA / Schnorr on SECP256K1). Push the skeptics which “the quantum hand wave as being more than 20 years old”, he argued that only “~ 2,000 logical qubits” could be sufficient to break the ECC-256 in a practical window, placing a credible attack in “2 to 6 years”. In a separate exchange, he framed the issues squarely: “Do you want 1 million dollars Bitcoin in 5 years, or $ 0?”
Related reading
The Edwards calendar closely follows a new range of research and messaging from the Pierre-Luc Dallaire-Demers industry, founder of Pauli Group, a quantum resistant silver startup. In a pre-impression and a public research thread in August, Dallaire-Démers and Co-Autors introduced ECDLP challenges classified on the Bitcoin curve and, after having translated logical circuits into physical costs in several architects corrected by mistake, placed “cryptanalystically respect” ECC-256 attacks in a large error “approximately 2027 to 2033”.
The Pauli group summed up the result clearly: “The first attack on the 256-bit ECC will occur with plausible between 2027-2033.” The company has also provocatively indicated via X: “PQC BTC will cost $ 1 million by 2030. ECC BTC will not.”
The basic risk vector is well established: once a Bitcoin address reveals its public key on the chain – by spending them or using inherited formats that exhibit the key – a sufficiently powerful quantum computer running the Shor algorithm could, in principle, derive the private key fairly quickly to steal funds.
Security researchers and industry teams note that the parts in the keys already exposed are the first online, while coins are still sitting behind chopped public keys (not revealed) are safer until they move. Several analyzes believe that a non-trivial part of the current BTC lies in the exposed key outings, including the first “Pay-to-Pubkey” era often associated with Satoshi. Edwards looked into this risk of tail, saying that “Satoshi’s parts will be due to a market” in the absence of a migration.
Related reading
Not everyone agrees on the speed of the clock. Certain conservative estimates still indicate that millions of qubits corrected by errors for practical and rapid ECDSA ruptures and standards organizations have published transition directives that implicitly assume a longer track.
At the end of 2024, the material circulated in migration sketched by the NIST / PQ ecosystem of vulnerable algorithms of approximately 2035 – a horizon that many security engineers consider realistic for wide computer systems, even if niche breakthroughs arrive earlier. The gap between the “thousands” compared to the “millions” of logical camps camps reflects rapidly evolving algorithmic optimizations, different error correction models and various hypotheses on the speeds of the door and code distances.
In particular, Edwards convey the message to Token2049 this week, where he should present “Double threat: Quantum & The Treasury Bubble” on Wednesday October 1 at 10:45 am, local time – positioning the quantum compromise and a “Bitcoin Treasury bubble” as the two dominant risks for the BTC in the cycle of the next cycle.
At the time of the press, BTC exchanged $ 112,150.
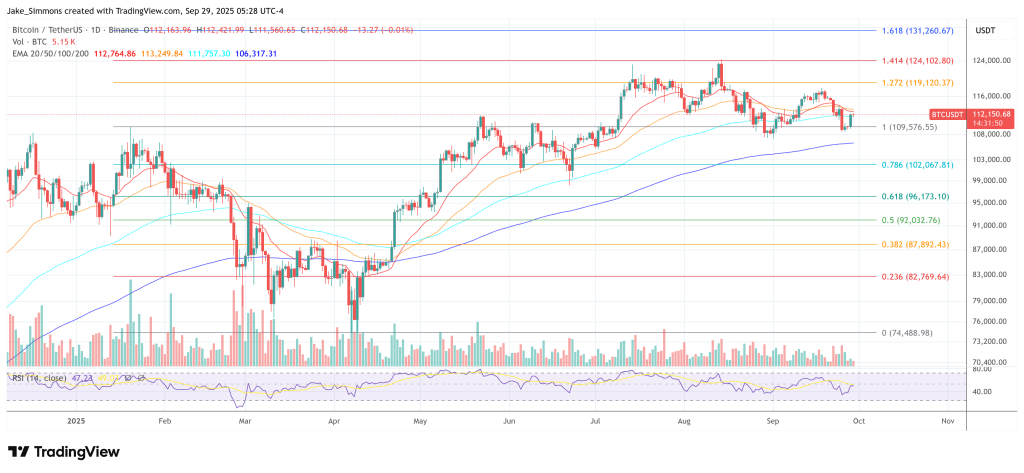
Star image created with dall.e, tradingView.com graphic


