



Close Menu
Altcoin ObserverAltcoin Observer
  • Regulation
  • Bitcoin
  • Altcoins
  • Market
  • Analysis
  • DeFi
  • Security
  • Ethereum
Categories
  • Altcoins (3,732)
  • Analysis (3,840)
  • Bitcoin (4,470)
  • Blockchain (2,157)
  • DeFi (2,623)
  • Ethereum (2,773)
  • Event (119)
  • Exclusive Deep Dive (1)
  • Landscape Ads (2)
  • Market (2,714)
  • Press Releases (12)
  • Reddit (2,847)
  • Regulation (2,474)
  • Security (4,103)
  • Thought Leadership (3)
  • Videos (44)
Hand picked
  • Uniswap RFC explores running private exchanges using v4 and UniswapX hooks
  • Australia targets Telegram a day after Russia indicts Durov
  • Bitcoin’s weak hands fold
  • Success Story: Jonathan Nichols’ Learning Journey with 101 Blockchains
  • Kraken Cyprus honored at the 14th Invest Cyprus International Investment Awards
We are social
  • Facebook
  • Twitter
  • Instagram
  • YouTube
Facebook X (Twitter) Instagram
  • About us
  • Disclaimer
  • Terms of service
  • Privacy policy
  • Contact us
Facebook X (Twitter) Instagram YouTube LinkedIn
Altcoin ObserverAltcoin Observer
  • Regulation
  • Bitcoin
  • Altcoins
  • Market
  • Analysis
  • DeFi
  • Security
  • Ethereum
Events
Altcoin ObserverAltcoin Observer
Home»Blockchain»Konni hackers target blockchain engineers with AI-created malware
Blockchain

Konni hackers target blockchain engineers with AI-created malware

January 28, 2026No Comments
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
Share
Facebook Twitter LinkedIn Pinterest Email


Konni hackers target blockchain engineers with AI-created malware

North Korean hacker group Konni (Opal Sleet, TA406) is using AI-generated PowerShell malware to target developers and engineers in the blockchain industry.

Believed to be associated with the APT37 and Kimsuky clusters, Konni has been active since at least 2014 and has been seen targeting organizations in South Korea, Russia, Ukraine, and various countries in Europe.

Based on samples analyzed by Check Point researchers, the threat actor’s latest campaign focuses on targets in the Asia-Pacific region, with the malware having been submitted from Japan, Australia, and India.
Ace

The attack begins when the victim receives a link hosted on Discord that provides a ZIP archive containing a decoy PDF and a malicious LNK shortcut file.

The LNK runs an embedded PowerShell loader that extracts a DOCX document and a CAB archive containing a PowerShell backdoor, two batch files, and a UAC bypass executable.

Launching the shortcut file opens the DOCX and executes a batch file included in the CAB file.
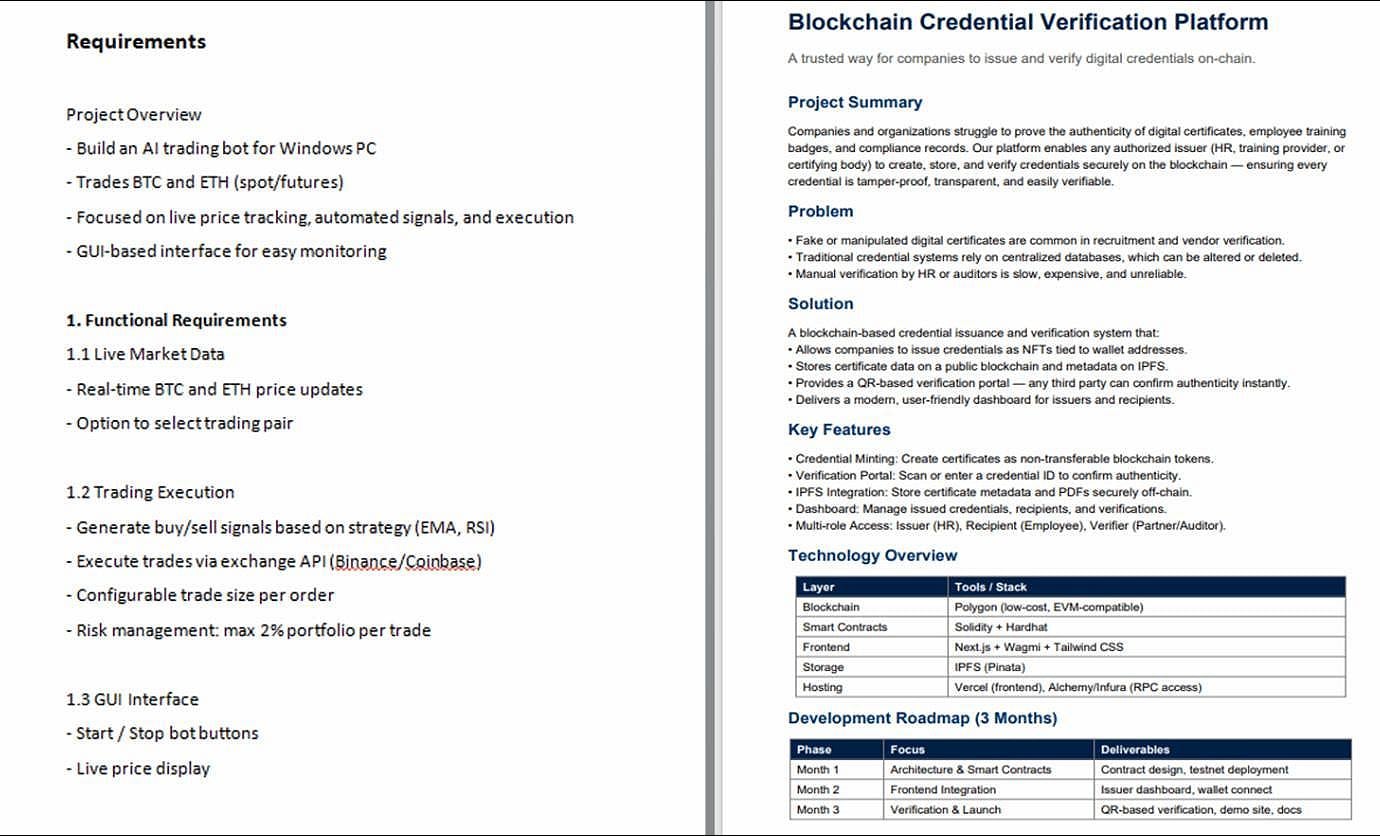
Lure used in phishing attack
The lure used in the phishing attack
Source: Checkpoint

The DOCX decoy document suggests that hackers want to compromise development environments, which could provide them with “access to sensitive assets, including infrastructure, API credentials, wallet access, and ultimately cryptocurrency holdings.”

The first batch file creates a staging directory for the backdoor and the second batch file, and creates an hourly scheduled task masquerading as a OneDrive startup task.

This task reads an XOR-encrypted PowerShell script from disk and decrypts it for execution in memory. Finally, it removes itself to erase the signs of infection.
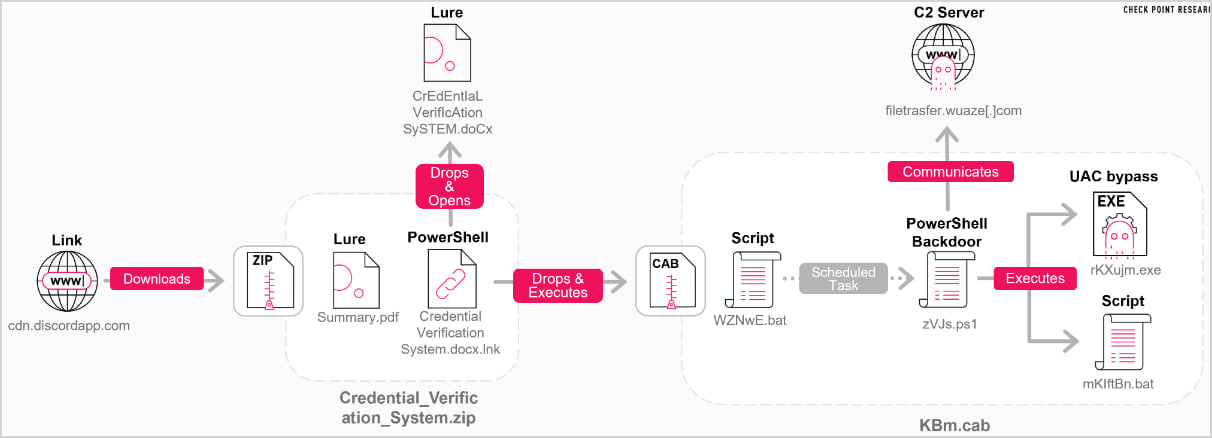
Latest infection chain
Source: Checkpoint

AI-generated backdoor

The PowerShell backdoor itself is heavily obfuscated using arithmetic-based string encoding, execution string reconstruction, and execution of final logic via “Invoke-Expression”.

The researchers say the PowerShell malware “strongly indicates AI-assisted development rather than traditional operator-created malware.”

Evidence leading to this conclusion includes the clear, structured documentation at the top of the script, which is unusual for malware development; its modular and refined layout; and the presence of a comment “# <– your permanent project UUID”.
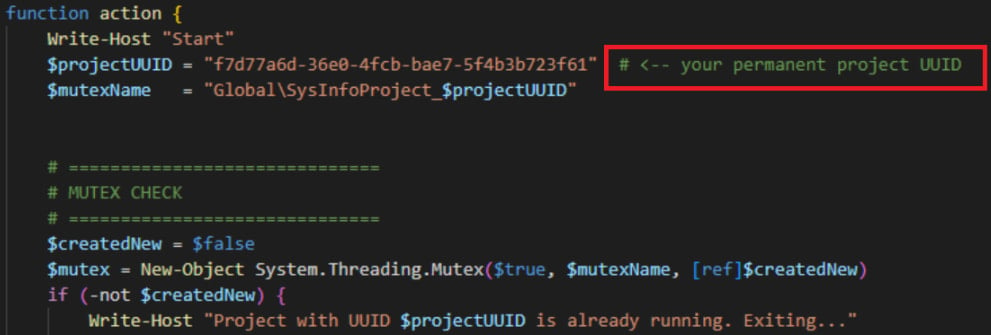
The exhibition chain
Source: Checkpoint

“This wording is very characteristic of LLM-generated code, where the model explicitly tells a human user how to customize a placeholder value,” Check Point explains.

“Such comments are commonly seen in AI-produced scripts and tutorials.”

Before execution, the malware performs checks of hardware, software, and user activity to ensure that it is not running in scanning environments, then generates a unique host ID.

Then, based on the execution privileges it has on the compromised host, it follows a separate path of action, as shown in the following diagram.
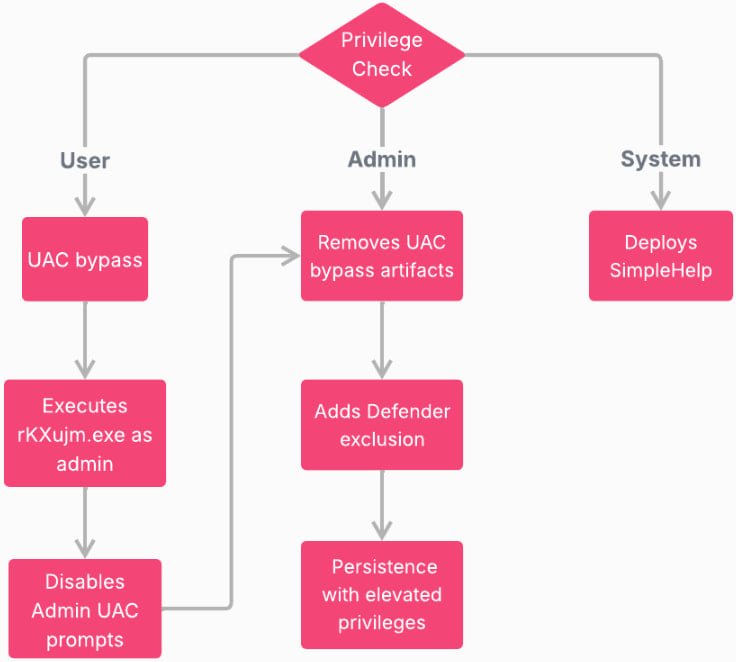
Privilege-based action diagram
Source: Checkpoint

Once the backdoor is fully operational on the infected device, it periodically contacts the command and control (C2) server to send basic host metadata and polls the server at random intervals.

If the C2 response contains PowerShell code, it turns it into a script block and executes it asynchronously through background tasks.

Check Point attributes these attacks to threat actor Konni based on previous launcher formats, overlapping file names and script names, and commonalities in execution chain structure with previous attacks.

Researchers have released Indicators of Compromise (IoCs) associated with this recent campaign to help defenders protect their assets.

Ace

Whether you want to clean up old keys or set guardrails for AI-generated code, this guide helps your team build securely from the start.

Get the cheat sheet and take the guesswork out of managing secrets.


Source link

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleDonald Trump Will not Consider Pardon for Sam Bankman-Fried: NYT
Next Article DeFi Technologies Announces Valor Receives UK Regulatory Approval and Begins Offering Certain Yield Crypto ETPs to UK Retail Investors Via London Stock Exchange Deutschland – English USA – English Deutschland – Deutsch

Related Posts

Blockchain

Japanese securities giant to issue $65 million worth of XRP-paying blockchain bonds – DL News

February 23, 2026
Blockchain

What is the .brave Blockchain domain and how it works

February 22, 2026
Blockchain

Why President Trump’s latest crypto scandal could be a disaster for the blockchain industry

February 22, 2026
Add A Comment
Leave A Reply Cancel Reply

Single Page Post
Share
  • Facebook
  • Twitter
  • Instagram
  • YouTube
Featured Content
Event

Dutch Blockchain Week 2026 strengthens position as Europe’s leading B2B blockchain event week

April 14, 2026

Amsterdam, April 2026 – Dutch Blockchain Week 2026 is rapidly evolving into one of Europe’s…

Event

Global Games Show Riyadh: The Ultimate Creator & Influencer Hub

March 31, 2026

The fast-evolving gaming ecosystem of Riyadh is powered by solid national investment, a flourishing esports…

1 2 3 … 82 Next
  • Facebook
  • Twitter
  • Instagram
  • YouTube

Australia targets Telegram a day after Russia indicts Durov

July 30, 2026

Ethena whales withdraw 102 million tokens from exchanges: has ENA selling pressure eased?

July 30, 2026

Audiera loses KEY support – can BEAT recover from 24% crash?

July 29, 2026
Facebook X (Twitter) Instagram LinkedIn
  • About us
  • Disclaimer
  • Terms of service
  • Privacy policy
  • Contact us
© 2026 Altcoin Observer. all rights reserved by Tech Team.

Type above and press Enter to search. Press Esc to cancel.

bitcoin
Bitcoin (BTC) $ 75,991.00
ethereum
Ethereum (ETH) $ 2,240.12
tether
Tether (USDT) $ 0.999021
bnb
BNB (BNB) $ 694.29
xrp
XRP (XRP) $ 1.18
usd-coin
USDC (USDC) $ 0.999567
solana
Solana (SOL) $ 90.27
tron
TRON (TRX) $ 0.318371
staked-ether
Lido Staked Ether (STETH) $ 2,265.05
figure-heloc
Figure Heloc (FIGR_HELOC) $ 1.03